EU AI Act Article 12
Eight-page evidence pack: system inventory, operational summary, material events, integrity proof, authority / authorisation evidence, manifest, sign-off block. Built against the regulation text + AI Office published guidance.
Anyone can build a log. The moat is turning the log into the answer the regulator, the insurer or the auditor actually accepts — in the format their procedures expect. Each pack carries the authority the agent was acting under at every action, and the recipient can verify offline that the pack is complete — nothing altered, nothing hidden.
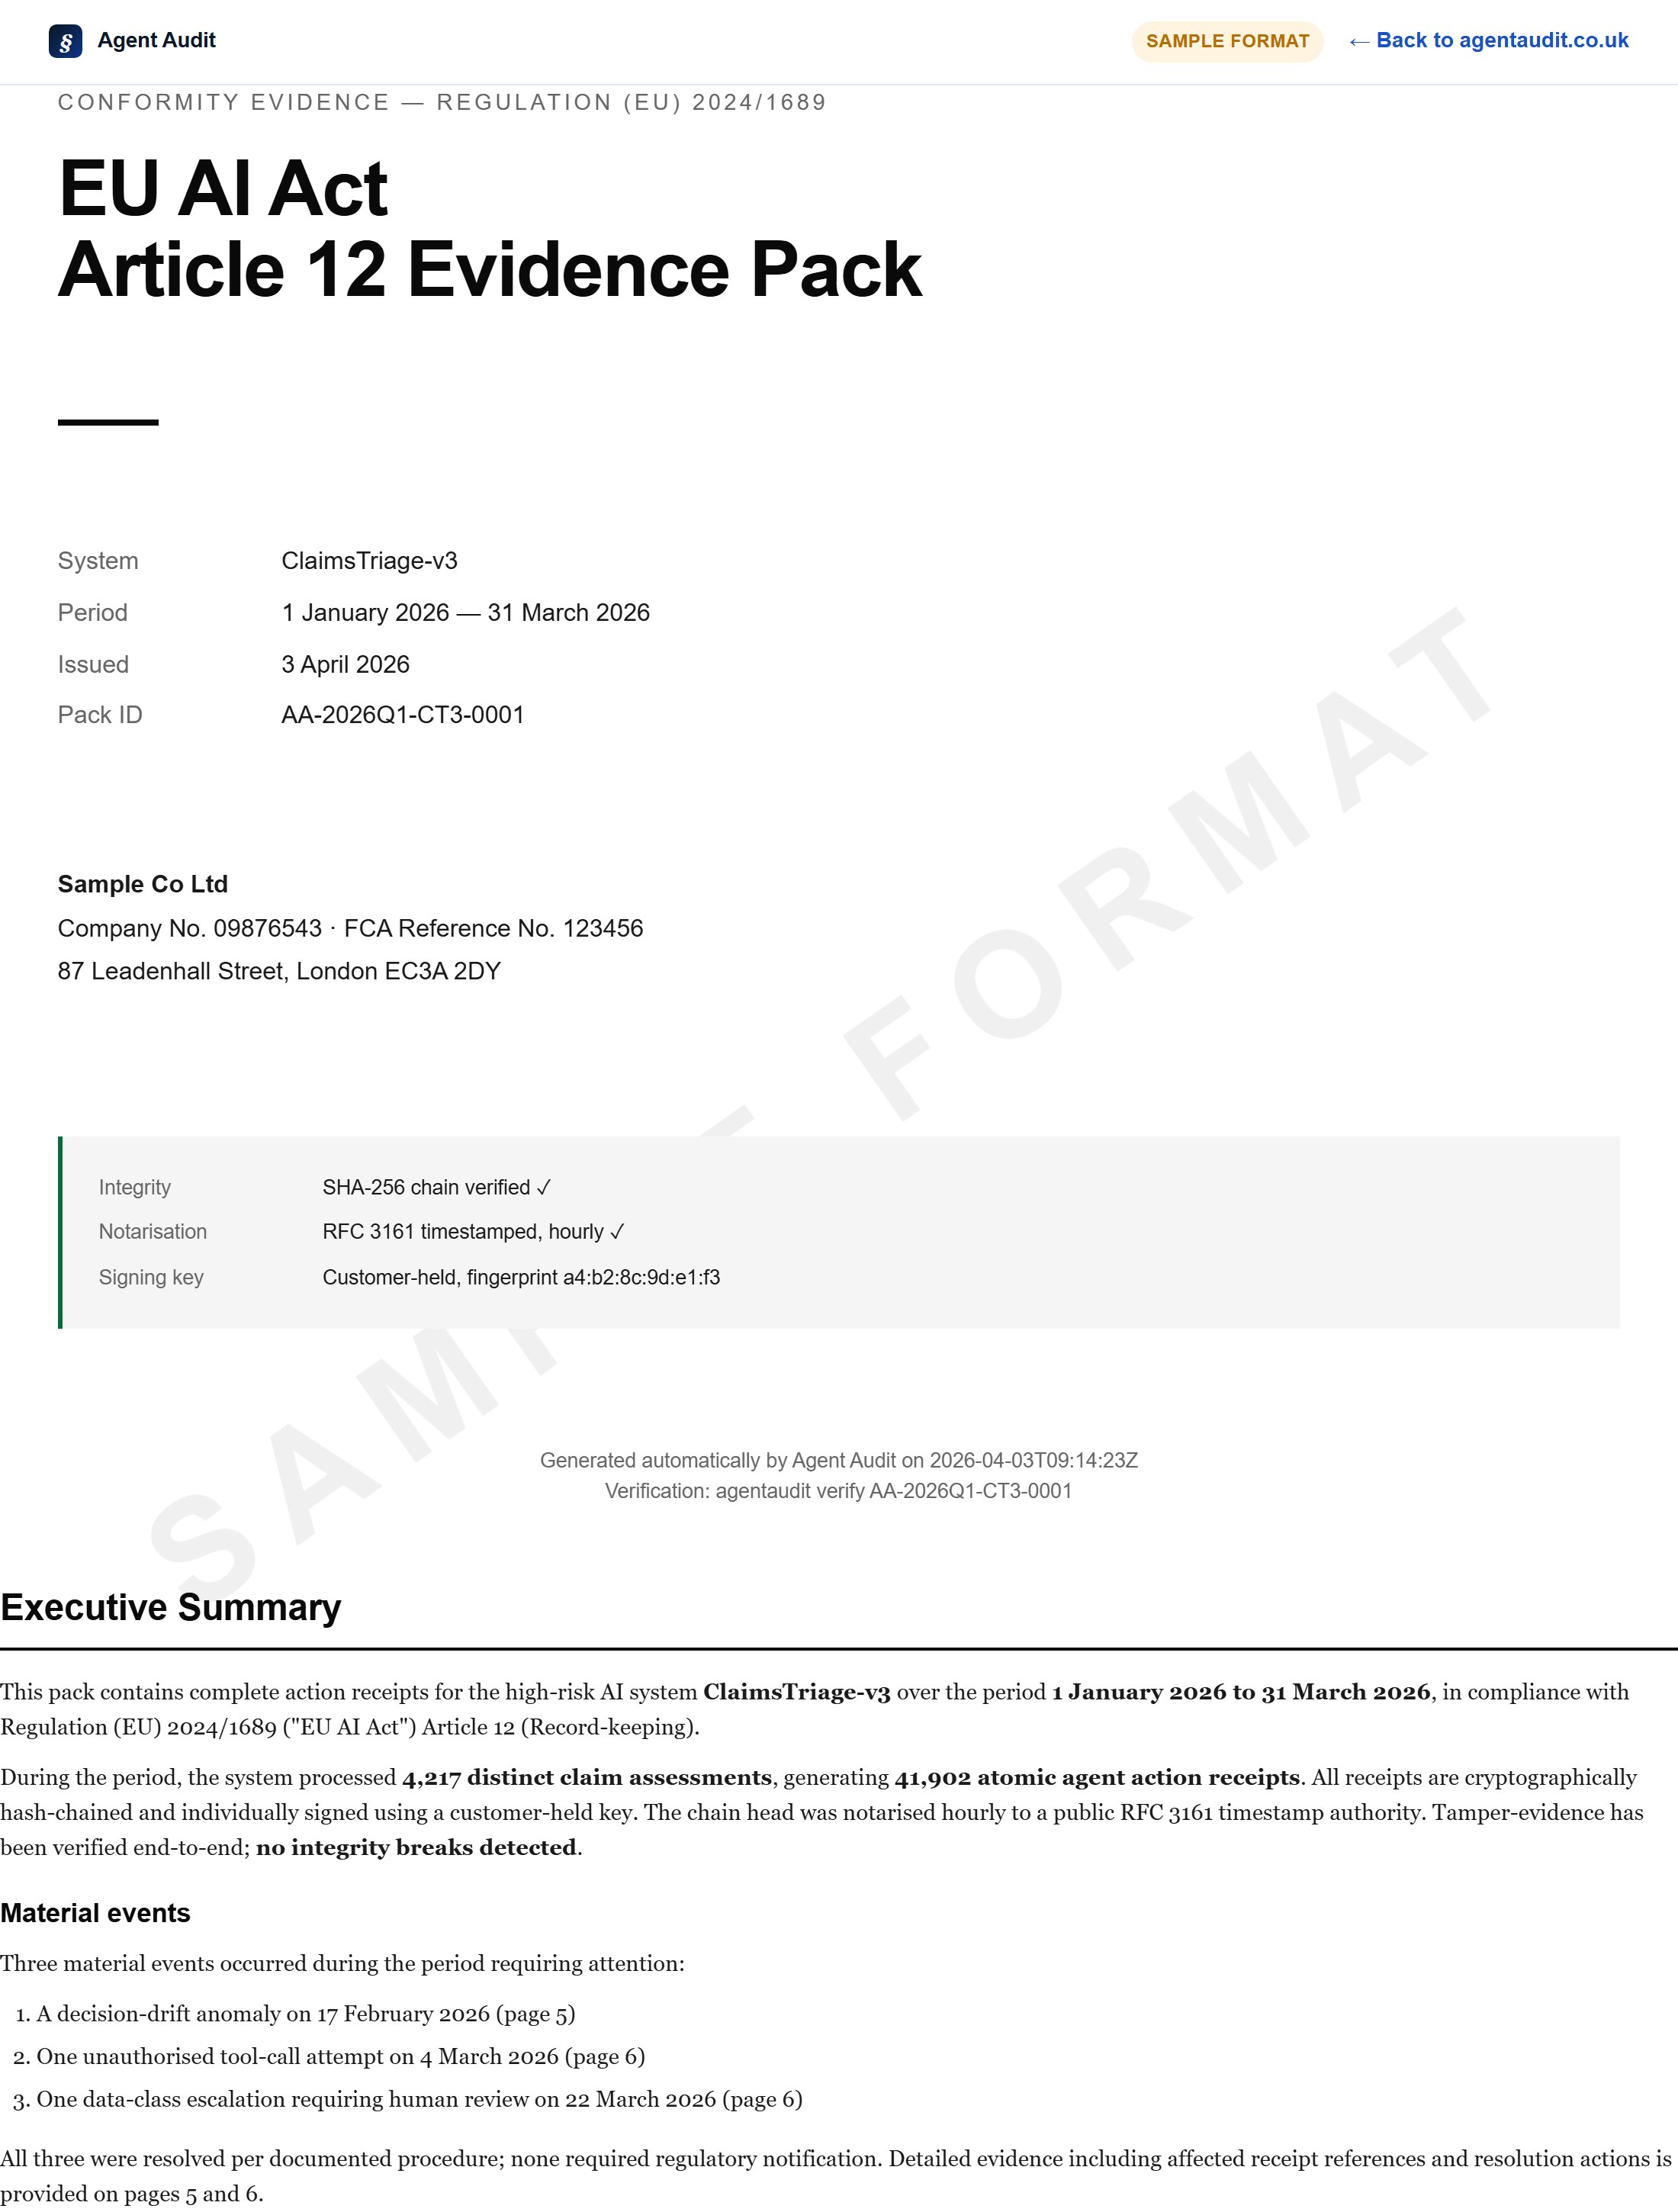
Real EU AI Act Article 12 pack · Open the full sample →
Eight-page evidence pack: system inventory, operational summary, material events, integrity proof, authority / authorisation evidence, manifest, sign-off block. Built against the regulation text + AI Office published guidance.
Every action involving a named data subject in a specified period, with categories of personal data, recipients, retention and DPO sign-off. UK GDPR Article 15.
Solely automated significant decisions under UK GDPR Articles 22A–22D (Data (Use and Access) Act 2025, in force 5 February 2026), with the Article 22C safeguards evidenced — information, representations, human intervention, contest — plus Article 22B special-category decisions.
Quarterly governance summary: anomaly review, material decisions logged, integrity status, key risk indicators. Built for the boardroom, not the dashboard.
Evidence pack for UK FCA-regulated firms demonstrating AI-driven service resilience and material event response. Maps SYSC 4, 8 and 15A.
Govern / Map / Measure / Manage evidence pack for US enterprise due diligence and federal contracting compliance.
Packaged evidence for cyber or E&O policy claim — incident timeline, affected receipts, integrity proof, RFC 3161 notarisation.
Evidence for automated decision-making technology (ADMT) in consequential decisions under Colorado's SB 26-189 (which repealed and replaced SB 24-205, effective 1 January 2027): advance notice, plain-language adverse-decision explanation within 30 days, correction and meaningful-human-review rights, and three-year recordkeeping.
Receipt evidence mapped to the UK's five cross-sectoral AI principles — safety/security/robustness, transparency & explainability, fairness, accountability & governance, contestability & redress — the principles-based, regulator-led UK approach applied by the FCA, ICO and others.
For UK healthcare customers — DSPT evidence pack covering AI-driven clinical decision support.
Whichever pack you send, the recipient can verify it offline — with no access to Agent Audit — and confirm it is both faithful and complete: nothing altered, nothing hidden, nothing backdated. That is the difference between proving it happened and proving the record you were handed is the whole record. The authority the agent was acting under at each action travels with the pack, so occurrence and authorisation can be read side by side.
Enterprise customers can commission custom packs for their jurisdiction. We co-develop with your compliance officer + external auditor.
Book a 30-minute walkthrough